Detect the Intruder Before the Damage Is Done
An attacker can get in without immediately looking like an attacker.
Managed Detection and Response helps law firms identify suspicious behavior after an attacker gains access to an account or device.
The Better Cybersecurity Question
Traditional security tools remain essential. But the cybersecurity challenge facing law firms has changed. Attackers can use legitimate employee credentials, trusted administrative tools and authorized technologies to move through an environment without immediately triggering a traditional malware alert.
Why Are Law Firms Attractive Cybersecurity Targets?
Law firms often maintain information that can be exceptionally valuable to cybercriminals. That makes cybersecurity more than an IT issue—it can become a client, operational and reputational issue.
Privileged Communications
Confidential client conversations, case information and litigation strategy.
Personal Information
Personally identifiable information belonging to clients, employees and other parties.
Financial Information
Banking details, payment instructions and other financial information.
Intellectual Property
Business plans, proprietary information, contracts and sensitive corporate materials.
Credentials
Accounts that may provide access to internal systems, cloud applications or client organizations.
Operational Leverage
Downtime can disrupt deadlines, communication and access to critical case information.
What Attacker Behaviors Can MDR Detect?
Many intrusions involve legitimate credentials, built-in administrative tools or approved technologies being used in an abnormal way. Context, sequence and behavior can reveal what a simple malware scan might miss.
A Stolen Account Starts Behaving Differently
An attorney who normally signs into Microsoft 365 from Houston during business hours suddenly generates unusual authentication activity or begins accessing resources in ways inconsistent with normal use.
Monitoring may identify unexpected locations, repeated failures, unusual privileged activity or changes in normal account behavior.
Credential Theft Begins
After compromising one computer, an attacker may attempt to obtain additional passwords or authentication information stored on the workstation.
Credential-dumping behavior can signal that an attacker is attempting to expand access.
Suspicious PowerShell Activity Appears
PowerShell is a legitimate Windows administration tool—which is one reason attackers may abuse it.
An investigation may examine who launched PowerShell, which command ran, which process started it and whether the activity fits normal behavior for that user or device.
The Attacker Moves Laterally
Attackers often need to move beyond the computer they initially compromised.
Monitoring may detect unusual endpoint-to-endpoint connections, abnormal server access, unexpected remote sessions or suspicious administrative-service activity.
Unexpected Remote-Access Software Appears
Remote-management tools serve legitimate purposes, but criminals can also use them.
A previously unseen remote-control application appearing unexpectedly on an attorney's laptop can warrant immediate investigation.
Security or Recovery Tools Are Disabled
Before ransomware deployment, an attacker may attempt to disable security software, remove logs, delete shadow copies, interfere with backups or stop security services.
Data Starts Moving Out
Modern ransomware attacks may include data theft before encryption. Abnormal outbound transfers can indicate that confidential information is being collected or exfiltrated.
Analysts Put the Signals Together
A single alert may be harmless. The value comes from combining telemetry, context and human analysis to determine whether multiple activities represent an active intrusion.
The practical question is not whether a product can generate alerts. It is whether the right systems are being monitored, the alert contains enough context to investigate, and a defined person or team owns the response.
Where Might MDR See an Attack Developing?
Imagine an employee enters credentials into a convincing phishing site. Nothing crashes. No ransom message appears. But behind the scenes, an attacker begins working.
Initial Access
Attacker: Uses stolen credentials.
Possible signal: Unusual authentication activity.
Execution
Attacker: Runs unexpected commands.
Possible signal: Suspicious PowerShell or command-line activity.
Credential Access
Attacker: Attempts to obtain more passwords.
Possible signal: Credential-dumping behavior.
Discovery
Attacker: Surveys systems and users.
Possible signal: Unusual enumeration activity.
Lateral Movement
Attacker: Connects to other computers.
Possible signal: Abnormal remote-service activity.
Remote Control
Attacker: Uses remote-control software.
Possible signal: Unexpected RMM execution.
Defense Evasion
Attacker: Weakens security or recovery.
Possible signal: Backup or security-service interference.
Data Exfiltration
Attacker: Transfers confidential data.
Possible signal: Abnormal outbound data movement.
Impact
Attacker: Deploys ransomware.
Possible signal: Rapid malicious file-system activity.
MDR Does Not Replace Your Other Security Controls
Managed Detection and Response should operate as one component of a layered cybersecurity strategy. Prevention remains important—but detection and response address the critical question of what happens when prevention does not stop an attacker.
Why 24/7 Monitoring Matters
A security alert generated in the middle of the night could be harmless—or it could indicate credential theft, lateral movement, data exfiltration or ransomware preparation.
Technology can generate an alert. Someone still needs to determine what it means.
MDR combines security telemetry and automated detection with security professionals who can investigate suspicious activity and, depending on the service arrangement and available integrations, take or coordinate response actions.
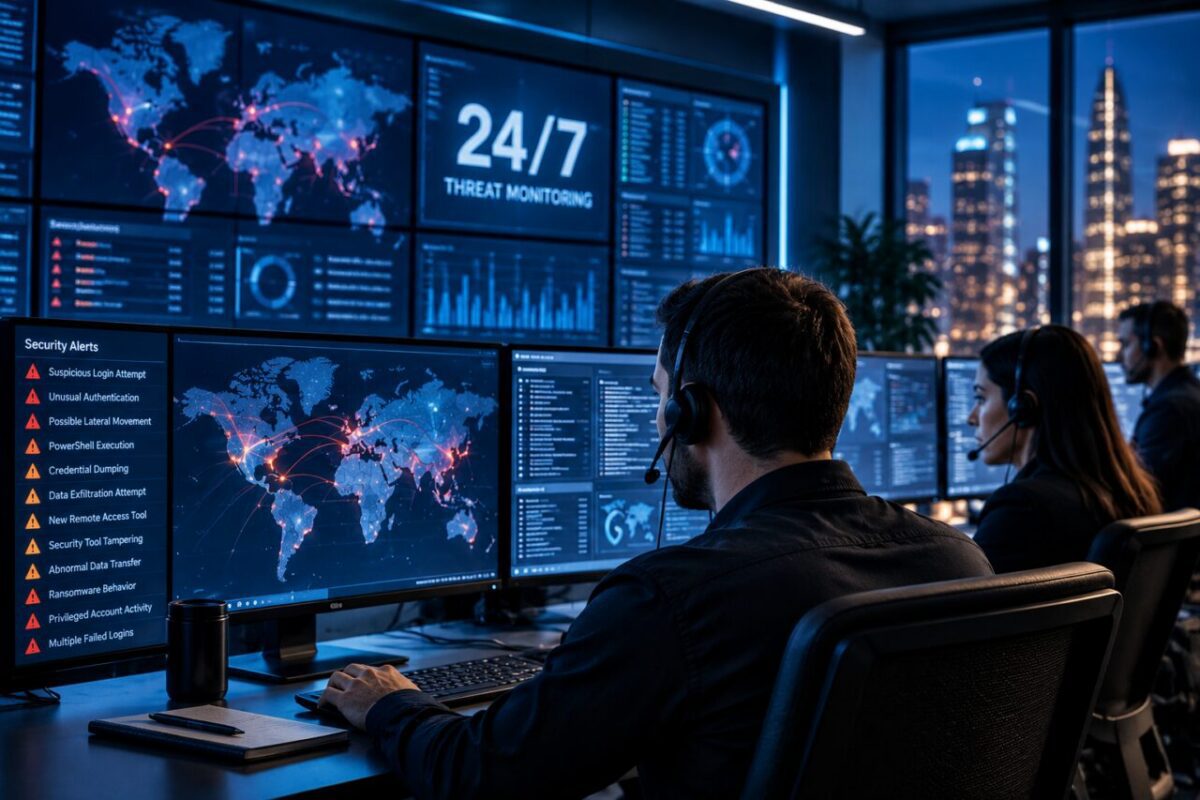
Law-firm leadership should understand not only who monitors alerts, but also what the monitoring team can do directly, what must be coordinated with the firm's IT provider, and which response permissions have been established in advance.
Five Questions Law Firm Leaders Should Ask About MDR
Which systems are actually monitored?
Detection depends on whether endpoints, identities, servers, cloud platforms, firewalls and applications are providing useful telemetry.
What attacker behaviors can you detect?
A product name or tool list does not tell leadership which behaviors can actually be identified and investigated.
Who investigates alerts at night and on weekends?
24/7 monitoring requires a defined analyst and response function, not simply automated alert generation.
What happens when suspicious activity is confirmed?
Understand how endpoint isolation, account disabling, escalation and coordination are handled.
What response actions are authorized in advance?
Response speed may depend on integrations, permissions, service arrangements and who has authority to act.
Managed Detection & Response
What does MDR mean in cybersecurity?
Is MDR the same as antivirus?
Can MDR detect ransomware before files are encrypted?
Why are law firms attractive cybersecurity targets?
What systems may need to feed an MDR service?
Does having MDR make a law firm completely secure?
Could Your Law Firm Detect These Behaviors Today?
Crescent IT Systems can review the security layers protecting your environment and discuss where 24/7/365 Managed Detection and Response may fit within your broader cybersecurity strategy.
Sources & Further Reading
American Bar Association — Cybersecurity: Back to Basics
CISA — #StopRansomware Guide
MITRE ATT&CK — Lateral Movement
MITRE ATT&CK — Exploitation of Remote Services
This article provides general cybersecurity information and is not legal, regulatory or compliance advice.